

RSA Authenticator (SecurID)
RSA SecurityCommunication
Scanned and Safe · Free
- Rating
- 3.3Out of 5
- Downloads
- 10.00M
- Android
- 10
Screenshots
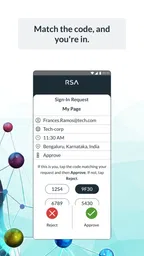
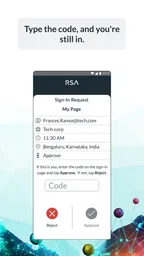
Analysis by Appxis
When I need to sign in while moving between home, work, and public Wi-Fi, an authenticator’s value comes down to a simple question: can I complete the check without adding another obstacle? RSA Authenticator (SecurID) is a free communication app from RSA Security, built for confirming identity with tools such as passkeys, biometrics, and one-time codes. That makes it most relevant when an organization or service already uses RSA for access, rather than as a universal replacement for every password or login method.
I would think of it as a companion to accounts that have been set up to use it. Installing the app alone does not secure every account on a phone; the service you are signing in to must support and enroll the authentication method. That distinction matters if you are comparing it with a general-purpose password manager or an authenticator you can independently connect to a wide range of personal accounts. For an employer or service that specifically relies on RSA, though, having the approval or code tool ready can make a protected sign-in less cumbersome.
Where connectivity changes the sign-in
The network’s effect depends on which authentication route a particular login uses. A one-time code and a prompt that asks you to approve a sign-in are different kinds of interaction, so I would not assume every route behaves the same way when a connection is weak. If a work login is time-sensitive, it is sensible to open the app before beginning the sign-in and check that the method you expect to use is available. That small habit can prevent the frustrating loop of switching between a login screen and a phone notification while a page waits.
A useful way to prepare is to distinguish the network you need for the account’s sign-in page from the connection involved in an app prompt. If you are travelling, for example, the company portal may load over one connection while your phone is on another. I would not treat a successful login in one situation as proof that every approval flow will work in every coverage condition. Follow the instructions shown by your organization, and keep a separate, authorized recovery route available for important work access.
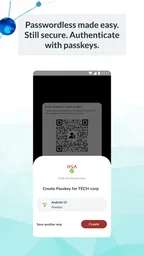
RSA Authenticator supports passkeys, biometrics, and OTP, but that does not mean every service offers all three through the app. The organization’s setup determines which options appear and what action you need to take. If you are unsure whether a particular sign-in requires a code, a biometric check, or a prompt, confirm the process with the administrator before you rely on it away from your usual network. This is more useful than guessing at the login screen, especially when a work task cannot wait.
On a phone during an ordinary day
In everyday use, the app makes most sense as a small part of a larger routine: your service asks for confirmation, you switch to the phone, complete the requested check, and return to the original screen. That is convenient when the phone is already in your hand. It is less seamless if you are juggling a call, trying to follow directions, or signing in on the same device that is supposed to show the approval. I would plan important work logins for a moment when I can focus on both screens rather than treating authentication as an invisible background task.
Picture arriving at a meeting and needing to open a work account on a laptop. The laptop asks for an additional check, so you reach for your phone and respond through the method your organization configured. If the prompt does not arrive promptly, repeatedly tapping the login button is unlikely to clarify what is wrong. I would first check that the original request is still active, then follow the service’s instructions and avoid approving a request I did not initiate. That last point is not a technical flourish: a prompt is a security decision, and convenience should never replace checking that the sign-in is yours.
More Stories While You Read
Keeping the phone accessible is also part of the trade-off. An authenticator can reduce the need to type a code from memory, but it makes the enrolled device important at the moment of sign-in. If you often leave your phone behind, use a device with a low battery, or travel where you may not have dependable service, discuss an approved backup method before you need one. I would not rely on a second phone or another person’s device unless the account owner or administrator has explicitly allowed that arrangement.
What to do when approval fails
A failed authentication step does not automatically mean the account or app is broken. The request could be delayed, the login session may have expired, or the method configured for that account may not be the one you expected. I would start by reading the message on the service’s sign-in page, then check whether the app is showing a request that matches the login I just initiated. If the details do not match, I would deny or ignore the request and contact the organization’s support team rather than approving it to get past the screen.
Changing phones deserves particular care. Because access is tied to an enrolled authentication setup, installing the app on a replacement device should not be treated as proof that existing sign-ins have transferred. Before wiping or giving away an old phone, ask the relevant service or administrator how to register the new one and what recovery steps apply. This is one of the less visible costs of relying on a phone-based authenticator: you need to think about device replacement while the old device is still available, not after you are locked out.
For a work account, the safest recovery plan is the one your organization recognizes. I would keep its help-desk route or account recovery instructions somewhere I can reach without signing in to the account that is failing. If the app is being used for a personal service, use that service’s own recovery process. An authenticator helps strengthen a login, but it is not a substitute for planning how to regain access if a device is lost, replaced, or unavailable.
Use it thoughtfully on mobile data
Authentication is a brief task, but it can still be worth being deliberate about when you are on a limited or unreliable connection. Avoid starting a sensitive sign-in while moving through a dead zone if you can wait until you have a stable connection, and do not share or forward an OTP as a shortcut for someone else. A code or approval is part of proving your identity; treating it like an ordinary message weakens the point of having the extra check.
I would also separate connection troubleshooting from privacy assumptions. A sign-in that stalls does not, by itself, tell you what information the app stores or how an organization manages account data. For questions about an employer’s authentication setup, use its IT guidance; for personal accounts, check the service’s own security and recovery instructions. That is a more reliable way to make a data-conscious choice than inferring a privacy policy from how quickly a code appears.
First Impressions and Interface
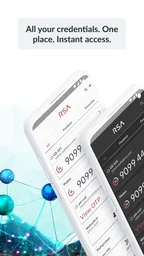
When I first opened the RSA Authenticator, I was greeted with a clean and straightforward interface. It's not cluttered, which is fantastic because who needs more chaos in their digital life, right? The setup process was a breeze, and even if technology isn't your forte, the app guides you through each step like a helpful buddy.
The app is an established option: it was released on May 24, 2011, and version 4.6.0.16 is the current version. It is rated Everyone and requires Android 9 or later, so the practical first check is compatibility with the phone you plan to enroll. I would also confirm that the organization or account you need to access actually supports RSA authentication. Those two checks matter more than downloading an authenticator simply because it sounds useful.
Its audience is reflected in the mixed public response: the average rating is 3.2 from around 18,000 ratings, alongside about 1,200 written reviews. More than 10 million installs suggest it is used at a substantial scale, but that does not guarantee a smooth experience with every organization’s setup. I would treat those figures as context, not as a substitute for checking whether it fits the sign-in process you actually use.
Features That Stand Out
Now, let's talk about the features. This app isn't just about generating codes; it's like a Swiss Army knife for digital security. You can use it for multi-factor authentication, adding an extra layer of security to your accounts. I've used it with several services, and the integration is seamless. No more fumbling around trying to remember passwords or codes!
The practical advantage is not that every login becomes effortless; it is that the second step can be handled through a method your account supports instead of relying on a password alone. The trade-off is that the service and its enrollment rules shape the experience. If you want one app to manage authentication for a broad collection of unrelated personal accounts, first check that those accounts accept this particular authenticator. If they do not, a general-purpose option may be a better fit.
One feature I really appreciated is the push notification option. Instead of manually entering a code, you get a prompt on your phone to approve or deny a login attempt. It's quick, efficient, and makes you feel like you're living in the future. Trust me, once you try it, there's no going back.
That convenience also calls for a careful habit: approve only a request that corresponds to a login you just started. If a prompt appears unexpectedly, do not treat it as a harmless interruption. A one-time code requires deliberate entry, while a push request asks for a decision; either way, the user still has to recognize a legitimate sign-in. I find that distinction more useful than judging an authenticator solely by how few taps it takes.
Security and Privacy
Security is the name of the game here. The app uses industry-standard encryption, so you know your data is in good hands. Plus, it works offline too, meaning you can generate codes even when you're off the grid. Whether you're in a coffee shop or hiking in the mountains, your accounts stay protected.
What I would emphasize in practice is not to generalize from one authentication method to another: network conditions can affect the sign-in experience differently depending on the route configured for an account. If you are about to travel or expect poor coverage, test the authorized process while you still have support available. I would not promise myself that every login will work offline, nor would I assume that a delayed prompt means I should approve a second one without checking its context.
Privacy is also a big deal. The app doesn't store your personal information, which is a relief in this digital age where data breaches seem to be a regular occurrence. You can rest easy knowing your information isn't floating around in cyberspace.
For data-conscious use, I would keep the authentication step focused: respond only to the login you initiated, avoid sharing codes, and use the account provider’s instructions for recovery or privacy questions. The app’s role is to support the sign-in; how an employer or service handles the account beyond that is a separate matter. This distinction helps set realistic expectations without confusing an authenticator with a password manager or a complete account-security plan.
Who will find it useful, and who may prefer another option
I would recommend it first to someone whose workplace or service has already chosen RSA. In that case, the question is not whether it replaces every security tool, but whether it makes the required sign-in routine manageable. It is also a sensible choice for users who want an additional authentication step and are comfortable keeping their enrolled phone close when access is needed.
I would skip it as a first choice if you want a single, flexible vault for passwords and authentication across a varied set of personal services. RSA Authenticator is centered on confirming access, not on organizing passwords. A password manager may serve that broader job better, while another authenticator may suit you if the services you use support it more directly. The best option is the one your account providers accept and that you can recover from safely.
There is also a real convenience-versus-dependence trade-off. A prompt can be faster than typing a code, but it depends on your recognizing the request and having the phone available. A code avoids waiting for an approval prompt, but still requires you to move between the login and the authenticator and enter it correctly. If you have a preferred method, check what your organization has enabled rather than assuming you can switch methods whenever you want.
Final Thoughts
All in all, the RSA Authenticator (SecurID) is a robust tool for anyone serious about digital security. It's user-friendly, packed with useful features, and keeps your information secure. If you're looking to step up your security game, I highly recommend giving it a try. Who knew staying secure could be so simple?
So, whether you're a tech guru or just someone who wants to keep their accounts safe, this app has got you covered. Go ahead, download it, and take control of your digital security. You'll thank me later!
My recommendation is strongest when RSA is already part of the account or workplace you need to access. Before relying on it for a critical login, confirm compatibility, understand the approved enrollment and recovery steps, and try the normal sign-in while you have a dependable connection. That preparation turns an authentication app from a last-minute hurdle into a predictable part of the day.
Connectivity shapes the experience, but it is not the only deciding factor. The key questions are whether your service supports the app, whether the available method suits your routine, and whether you know what to do if the phone is unavailable. For the right setup, it can be a straightforward security companion; for someone seeking a universal password-and-code manager, a different tool is likely a better match.
Pros
- Enhances account security significantly.
- Supports multi-factor authentication seamlessly.
- User-friendly interface and easy setup.
- Works offline for added convenience.
- Compatible with various platforms and apps.
Cons
- Limited customer support availability.
- Occasional app crashes reported by users.
- No backup option for lost tokens.
- Frequent updates may disrupt functionality.
- Complexity for non-tech-savvy users.
RSA Authenticator (SecurID) FAQ
What is RSA Authenticator (SecurID) and how does it work?
RSA Authenticator, also known as SecurID, is a multi-factor authentication app designed to enhance the security of user logins. It provides a second layer of security by generating a one-time passcode (OTP) every 60 seconds, which users need to enter along with their regular password. This makes unauthorized access significantly harder, as knowing the password alone is not enough to gain entry.
Is RSA Authenticator compatible with all devices and operating systems?
RSA Authenticator is widely compatible with most modern Android and iOS devices. However, it's important to ensure your device meets the minimum OS requirements specified by the app. Users should also check for any specific compatibility issues, especially if using older devices or operating systems, to ensure smooth functionality.
How do I set up RSA Authenticator on my device?
Setting up RSA Authenticator involves downloading the app from the Google Play Store or Apple App Store and linking it to your online accounts that support SecurID. Typically, this requires scanning a QR code provided by the service you are securing, or manually entering a secret key. Follow the in-app instructions carefully to complete the setup process.
What should I do if I lose access to my RSA Authenticator?
If you lose access to your RSA Authenticator, it's crucial to have backup options prepared. Most services allow you to set up recovery codes or an alternative authentication method. Contacting your IT administrator or the service provider for help regaining access is also advisable. Keep backup codes secure and accessible.
Are there any costs involved in using RSA Authenticator?
The RSA Authenticator app itself is generally free to download and use. However, some services using RSA SecurID for authentication might incur additional costs, especially in enterprise settings. It's recommended to check with your organization or service provider to understand any potential charges associated with using multi-factor authentication.
Read This Page in Another Language
Other Picks in This Category

WhatsApp Messenger
WhatsApp LLC 4.6 Out of 5

Gmail
Google LLC 4.1 Out of 5

Google Meet
Google LLC 4.4 Out of 5

Google Messages
Google LLC 4.2 Out of 5
More Communication Reviews

Google Chrome
Google LLC 4.1 Out of 5

Hangouts
Google LLC 4.1 Out of 5

Carrier Services
Google LLC 4.2 Out of 5

Contacts
Google LLC 4.3 Out of 5

Messenger
Meta Platforms, Inc. 4.7 Out of 5

UC Browser-Safe, Fast, Private
UCWeb Singapore Pte. Ltd. 4.4 Out of 5
About This Listing
- Developer
- RSA Security
- Package Name
- com.rsa.securidapp
- Version
- 4.7.1.1
- Android
- 10
- Price
- Free
This site provides independent information about third-party apps. We do not own, develop, or distribute them. Names, logos, and trademarks belong to their respective owners. Developer details are for reference only. For more information, please contact the developer at MobileAuthenticatorFeedback@rsa.com, visit https://www.securid.com/en-us/products/one-time-password-authentication, or view the https://www.rsa.com/privacy/.